Mafiree logo
  • About
  • Services
  • Blogs
  • Careers
  • Products
    • orbit logo Orbit
    • streamer logo Xstreami
  • Contact
Schedule a Call
Menu
  • About
  • Services
  • Blogs
  • Careers
  • Products
    • orbit logo Orbit
    • streamer logo Xstreami
  • Contact
  • Schedule a Call
Database
Database Managed Database Services
MySQL MySQL
MySQL Consulting
MySQL Migration Services
MySQL Optimization & Query Tuning
MySQL Database Administration
MySQL Backup & Recovery
MySQL Security & Maintenance
MySQL Cloud Services (AWS RDS, Aurora, Google Cloud SQL, Azure)
MySQL for Ecommerce
MySQL High Availability & Replication
MongoDB MongoDB
MongoDB Consulting
MongoDB Migration Services
MongoDB Optimization & Query Tuning
MongoDB Database Administration
MongoDB Backup & Recovery
MongoDB Security & Maintenance
MongoDB Cloud (Atlas)
MongoDB Solutions by Industry
MongoDB High Availability & Replication
PostgreSQL PostgreSQL
PostgreSQL Consulting
PostgreSQL Migration & Upgrades
Performance Tuning & Query Optimization
PostgreSQL Administration & Managed Services
High Availability, Clustering & Replication
PostgreSQL Backup, Recovery & Disaster Planning
PostgreSQL Security, Compliance & Auditing
PostgreSQL for Analytics & Data Warehousing
PostgreSQL on Cloud & Containers
PostgreSQL Extensions & Open-Source Integrations
PostgreSQL for Every Industry
SQL Server MSSQL
MSSQL Consulting
MSSQL Migration Services
MSSQL Optimization & Query Tuning Services
MSSQL Database Administration Services
MSSQL Backup & Recovery Services
MSSQL High Availability & Replication Services
MSSQL Security & Compliance Services
MSSQL Performance Monitoring & Health Checks
MSSQL Solutions by Industry
Aerospike Aerospike
Aerospike Consulting
Aerospike Migration Services
Aerospike Performance Optimization & Tuning
Aerospike Backup & Recovery
Aerospike High Availability
Aerospike Cloud & Hybrid Deployments
Aerospike for Real-Time Applications (AdTech, FinTech, Retail, IoT)
Clickhouse Clickhouse
ClickHouse Consulting
ClickHouse Migration Services
ClickHouse Optimization & Query Tuning
ClickHouse Database Administration
ClickHouse Backup & Recovery
ClickHouse Security & Maintenance
ClickHouse Cloud Services (ClickHouse Cloud, AWS, GCP, Azure)
ClickHouse Solutions by Industry
ClickHouse High Availability & Replication
TiDB TiDB
TiDB Consulting
TiDB Administration & Maintenance
TiDB Security and Privacy Maintenance
TiDB Performance & Query Optimization
TiDB Migration Services
TiDB Backup & Disaster Recovery
TiDB High Availability Solutions
TiDB Solutions by Industry
TiDB Cloud Services
ScyllaDB ScyllaDB
ScyllaDB Consulting
ScyllaDB Administration & Maintenance
ScyllaDB Security and Privacy Maintenance
ScyllaDB Performance & Query Optimization
ScyllaDB Migration Services
ScyllaDB Backup & Disaster Recovery
ScyllaDB High Availability Solutions
ScyllaDB Solutions by Industry
ScyllaDB Cloud Services
DevOps
DevOps DevOps Services
Version Control Version Control
Kubernetes Kubernetes
Infrastructure Infrastructure Management
Web Servers Web Servers
Networking
Networking Networking Services
Basic Basic
Advanced Advanced
MySQL MySQL
MongoDB MongoDB
PostgreSQL PostgreSQL
MSSQL MSSQL
Aerospike Aerospike
Clickhouse Clickhouse
TiDB TiDB
ScyllaDB ScyllaDB
Version Control Version Control
Kubernetes Kubernetes
Infrastructure Infrastructure Management
Web Servers Web Servers
Basic Basic
Advanced Advanced
MySQL Consulting
MySQL Migration Services
MySQL Optimization & Query Tuning
MySQL Database Administration
MySQL Backup & Recovery
MySQL Security & Maintenance
MySQL Cloud Services (AWS RDS, Aurora, Google Cloud SQL, Azure)
MySQL for Ecommerce
MySQL High Availability & Replication
MongoDB Consulting
MongoDB Migration Services
MongoDB Optimization & Query Tuning
MongoDB Database Administration
MongoDB Backup & Recovery
MongoDB Security & Maintenance
MongoDB Cloud (Atlas)
MongoDB Solutions by Industry
MongoDB High Availability & Replication
PostgreSQL Consulting
PostgreSQL Migration & Upgrades
Performance Tuning & Query Optimization
PostgreSQL Administration & Managed Services
High Availability, Clustering & Replication
PostgreSQL Backup, Recovery & Disaster Planning
PostgreSQL Security, Compliance & Auditing
PostgreSQL for Analytics & Data Warehousing
PostgreSQL on Cloud & Containers
PostgreSQL Extensions & Open-Source Integrations
PostgreSQL for Every Industry
MSSQL Consulting
MSSQL Migration Services
MSSQL Optimization & Query Tuning Services
MSSQL Database Administration Services
MSSQL Backup & Recovery Services
MSSQL High Availability & Replication Services
MSSQL Security & Compliance Services
MSSQL Performance Monitoring & Health Checks
MSSQL Solutions by Industry
Aerospike Consulting
Aerospike Migration Services
Aerospike Performance Optimization & Tuning
Aerospike Backup & Recovery
Aerospike High Availability
Aerospike Cloud & Hybrid Deployments
Aerospike for Real-Time Applications (AdTech, FinTech, Retail, IoT)
ClickHouse Consulting
ClickHouse Migration Services
ClickHouse Optimization & Query Tuning
ClickHouse Database Administration
ClickHouse Backup & Recovery
ClickHouse Security & Maintenance
ClickHouse Cloud Services (ClickHouse Cloud, AWS, GCP, Azure)
ClickHouse Solutions by Industry
ClickHouse High Availability & Replication
TiDB Consulting
TiDB Administration & Maintenance
TiDB Security and Privacy Maintenance
TiDB Performance & Query Optimization
TiDB Migration Services
TiDB Backup & Disaster Recovery
TiDB High Availability Solutions
TiDB Solutions by Industry
TiDB Cloud Services
ScyllaDB Consulting
ScyllaDB Administration & Maintenance
ScyllaDB Security and Privacy Maintenance
ScyllaDB Performance & Query Optimization
ScyllaDB Migration Services
ScyllaDB Backup & Disaster Recovery
ScyllaDB High Availability Solutions
ScyllaDB Solutions by Industry
ScyllaDB Cloud Services
  1. Home
  2. > Blogs
  3. > MySQL
  4. > Column-Level Security: Enterprise Data Protection Without the Infrastructure Overhead

Column-Level Security: Enterprise Data Protection Without the Infrastructure Overhead

Column-level security is a native database feature that restricts access to specific table columns by user role. Mafiree implemented this for a client as a cost-effective replacement for a planned CDC replication architecture that existed solely to strip sensitive columns. The result: zero additional infrastructure, single source of truth, full GDPR/HIPAA compliance posture, and validated in production with no performance impact.

sukan May 13, 2026

Subscribe for email updates

Summarize with AI: ChatGPT Google AI Perplexity Claude Grok
Column-Level Security: Protect Sensitive Data Without CDC Replication Costs

Column-level security is one of the most underused features in relational databases — and one of the most cost-effective ways to protect sensitive data. When a client came to Mafiree needing to restrict PII, financial fields, and confidential columns from unauthorized users, the instinct was to replicate tables via CDC and strip out the sensitive columns at the pipeline level. That instinct was expensive. The right answer was built into the database all along.

In this guide, Mafiree's database consultants walk through exactly how column-level security works, why it outperforms CDC-based approaches for access control, and how to implement it in four straightforward steps — with zero additional infrastructure and full compliance coverage for GDPR, CCPA, and HIPAA.

Key Takeaways
  • Column-level security restricts access to specific database columns by user role — no data duplication required.
  • It replaces costly CDC replication architectures used purely for access segregation.
  • Native to most relational databases — no new tools, licenses, or infrastructure.
  • Supports GDPR, CCPA, and HIPAA compliance by enforcing field-level data minimisation.
  • Validated in production: sensitive columns fully restricted, zero performance degradation observed.

The Problem: When Too Many Users See Too Much Data

A common architectural debt in growing organisations is overly permissive database access. Tables designed for one team get shared across departments, and before long, support agents can see salary fields, junior developers can query national ID numbers, and reporting users have full visibility into financial records they were never meant to access.

This isn't just a security concern — it's an active compliance liability. Under GDPR's data minimisation principle, users should only access the data necessary for their role. CCPA imposes similar restrictions on personal information. HIPAA mandates strict controls over protected health information. Column-level exposure to unauthorised users can trigger audit failures and regulatory penalties.

The instinctive engineering response — replicate the table, strip the sensitive columns in the pipeline — solves the symptom but creates new problems.

Why CDC Replication Is the Wrong Tool for Access Control

Change Data Capture (CDC) replication is a powerful tool for data pipelines, real-time analytics, and system integration. It's not the right tool for restricting what columns a user can see.

When teams use CDC to replicate tables and exclude sensitive columns, they're solving an access control problem with an infrastructure solution. The cost compounds quickly:

CDC Replication for Access Control Column-Level Security (Native)
Additional infrastructure required (CDC engine, target DB) Zero new infrastructure
Replication lag — data may be stale Single source of truth, always current
Storage duplication for each restricted view No additional storage
High operational complexity — two systems to maintain Managed through native DB roles
Synchronisation failures create data gaps No sync — restrictions applied at query time
Scales poorly as column restrictions grow Easily extended to new tables and columns

The fundamental issue is that CDC replication creates a copy of your data to solve an access problem. Column-level security solves access problems at the access layer — which is exactly where they belong.

How Column-Level Security Works

Column-level access control is a feature of all major relational databases including MySQL, MariaDB, PostgreSQL, and SQL Server. Instead of controlling access at the table level (GRANT SELECT on table), it lets you control access at the column level (GRANT SELECT on specific columns only).

When a user without column-level privileges runs a query that touches a restricted field — whether directly or via SELECT * — the database engine denies access to that column's data. Authorised users see everything. Unauthorised users see everything except the protected fields.

Database Support: Column-level GRANT is supported in MySQL 8.0+, MariaDB 10.5+, PostgreSQL (via column-level privileges), and SQL Server (via GRANT/DENY at column level). Check your engine's documentation for syntax specifics. MySQL GRANT reference →

What Gets Restricted

Column-level security is best applied to fields that carry genuine sensitivity risk:

  • PII fields — national ID, passport, date of birth, address
  • Financial data — salary, account numbers, credit scores
  • Health information — medical records, diagnosis codes, prescription data
  • Authentication data — password hashes, API keys, tokens
  • Commercially sensitive fields — margin percentages, contract values, pricing tiers

Implementing Column-Level Security: A Four-Step Process

Mafiree's implementation follows a clean four-step process. It's auditable, testable, and reversible. No downtime required.

  1. Define Roles Based on Access Requirements Map out which business functions genuinely need access to each sensitive column. Create database roles that reflect those access levels — for example, role_hr_full, role_reporting_restricted, role_support_view. Keep role definitions tight and purpose-specific.
  2. Grant Column-Level Privileges to Each Role Use your database's native GRANT syntax to assign column-level SELECT (and UPDATE if needed) privileges to the appropriate roles. Sensitive columns are explicitly withheld from roles that don't require them. In MySQL/MariaDB, this looks like: GRANT SELECT (col1, col2) ON db.table TO 'role_name';
  3. Assign Users to Roles Map each database user to their appropriate role based on job function and clearance level. A user can hold multiple roles. Role assignment is the only ongoing maintenance step — when someone changes team, you update their role, not their column permissions.
  4. Validate with Comprehensive Testing Test access for each role explicitly. Verify that unauthorised users cannot access restricted columns — directly, via SELECT *, or through views. Confirm that authorised users retain full expected access. Document test results for your audit trail.

Example: MySQL Column-Level Grant

-- Create roles
CREATE ROLE 'role_hr_full';
CREATE ROLE 'role_reporting_restricted';

-- Full access for HR role
GRANT SELECT ON employees TO 'role_hr_full';

-- Restricted access for reporting — sensitive columns excluded
GRANT SELECT (employee_id, department, job_title, hire_date)
  ON employees TO 'role_reporting_restricted';

-- Assign users to roles
GRANT 'role_hr_full' TO 'hr_user'@'%';
GRANT 'role_reporting_restricted' TO 'analyst_user'@'%';

-- Activate role for session
SET DEFAULT ROLE ALL TO 'analyst_user'@'%';
Need Help Designing Your Database Access Control Strategy?

Mafiree's DBA consultants have implemented column-level security across MySQL, MariaDB, and PostgreSQL environments. We'll assess your current permissions model and implement a clean, auditable solution.

Talk to a Mafiree DBA Expert MySQL DBA Services

Key Benefits of Column-Level Security

When implemented correctly, column-level access control delivers significant advantages across security, cost, and compliance dimensions:

▶ Zero Infrastructure Cost

No additional servers, CDC pipelines, or replication tools. Column-level restrictions are enforced by the database engine you already run.

▶ Single Source of Truth

All users query the same table. No synchronisation lag, no data consistency issues, no divergent copies to reconcile.

▶ Native Performance

Access checks happen at the database engine level with negligible overhead. No pipeline latency, no transformation cost.

▶ Compliance-Ready

Satisfies data minimisation requirements under GDPR, CCPA, and HIPAA. Provides a clear, auditable permission model.

▶ Scalable Governance

Adding restrictions to new columns or tables requires only role updates — no pipeline reconfiguration or infrastructure changes.

▶ Reduced Operational Complexity

One system to maintain instead of two. Fewer failure points, simpler runbooks, lower on-call burden for your DBA team.

Real-World Validation: What Mafiree's Testing Confirmed

Mafiree implemented and validated column-level security for a client operating a multi-team database environment with sensitive employee and financial data. The solution replaced a planned CDC replication architecture that would have added significant infrastructure and operational overhead.

Metrics are from a real-world engagement; client identity withheld under NDA.

✓ Sensitive columns successfully restricted from all unauthorised user roles
✓ Authorised users retained full, uninterrupted access to all required data
✓ Unauthorised users confirmed unable to access protected fields via direct query or SELECT *
✓ Solution met all stated security and compliance requirements
✓ Zero performance degradation observed under production load

When Column-Level Security Is — and Isn't — the Right Fit

Column-level security solves one problem well: restricting which users can read (or modify) specific fields within a table. It's the right choice when:

  • Multiple teams share a table but need different column visibility
  • You're using CDC replication purely to strip sensitive columns — not for actual data pipeline needs
  • Compliance mandates field-level access controls for PII, PHI, or financial data
  • You want a clean, auditable permissions model without architectural complexity

It's not a substitute for row-level security (restricting which rows a user can see), encryption at rest, or network-level controls. A robust data security posture combines multiple layers — column-level access control is one critical component of that stack.

Column-level security vs. database views: Views can also restrict column visibility, but they require maintaining view definitions for each access pattern and can be bypassed if users have direct table access. Column-level GRANT works at the privilege layer — it's enforced regardless of how the query reaches the table.

Conclusion: Stop Over-Engineering Access Control

Column-level security is a native, production-proven mechanism for restricting sensitive data access. It eliminates the need for CDC replication architectures built solely to segregate column visibility, delivering the same protection — better protection, in fact — at a fraction of the operational cost.

Mafiree's recommendation is straightforward: if your reason for replicating data is to control what columns different users can see, stop replicating and start using the access control tools your database already ships with. Define roles, grant column-level privileges, assign users, and validate. The compliance posture improves. The infrastructure footprint shrinks. The operational complexity drops.

Smart security doesn't require expensive infrastructure. It requires using the right tool for the right problem — which is exactly what Mafiree's database consultants help organisations do every day.

Related Mafiree Resources
  • MariaDB Evolution: Latest Features and What It Offers Compared to MySQL
  • Mafiree MySQL DBA Services — Managed Security and Performance
  • Mafiree MariaDB Services — Consulting and Migration Support
  • Database Migration Services — Secure, Zero-Downtime Migrations
Ready to Implement Column-Level Security?

Mafiree's database consultants will audit your current permissions model, design a role-based access architecture, and implement column-level security across your tables — with full validation and audit documentation included.

Get a Free Consultation

FAQ

Column-level security (also called column-level access control) is a database feature that lets administrators restrict which users or roles can read or modify specific columns within a table. Unlike table-level permissions, column-level grants apply at the field level — authorised users see all columns while unauthorised users see only the columns they have been explicitly granted access to.
Column-level access control is supported natively in MySQL 8.0+, MariaDB 10.5+, PostgreSQL, Microsoft SQL Server, and Oracle Database. The syntax varies slightly between engines, but the underlying mechanism is consistent across all major RDBMS platforms.
GDPR's data minimisation principle requires that users only access personal data necessary for their specific purpose. Column-level security directly enforces this by ensuring sensitive fields are only accessible to roles that genuinely need them, creating an auditable permission structure that satisfies regulatory requirements and helps pass internal and external audits.
Column-level GRANT is generally more robust than views for access control. Views require maintaining separate definitions for each access pattern and can be bypassed if users also hold direct table-level privileges. Column-level security is enforced at the privilege layer regardless of how a query reaches the table.
In Mafiree's testing, zero performance degradation was observed after implementing column-level security in production. Database engines evaluate column-level privileges at query planning with negligible overhead. CDC-based replication alternatives introduce latency and storage duplication that native column restrictions avoid entirely.
For a well-defined table with clear access requirements, Mafiree typically implements and validates column-level security within a single engagement. The four-step process can be completed in hours for straightforward configurations. Larger environments with many tables or complex role hierarchies may require a phased rollout.

Author Bio

sukan

Sukan is Database Team Lead at Mafiree with over a decade of experience in database systems, architecture, and performance optimization. He specializes in MySQL, MongoDB, TiDB, and ClickHouse, developing architectural improvements that make data platforms faster, more efficient, and cost-effective. Sukan writes about practical database engineering topics, real-world performance tuning, data replication, and high-scale system design, drawing from extensive hands-on experience solving complex technical challenges.

Leave a Comment

Related Blogs

MySQL Incident Response: When Does Slow Response Signal a Support Model Gap?

Slow MySQL incident resolution is often a symptom of a weak support model—not just a technical problem. Learn how to identify gaps in escalation, monitoring, automation, DBA expertise, and post-incident reviews before they lead to recurring downtime.

  42 views
MySQL Deadlock Analysis: Diagnosing and Resolving Lock Contention in High-Concurrency Workloads

A MySQL deadlock occurs when two or more transactions hold locks that each other needs, creating a circular dependency that prevents them from proceeding. InnoDB detects the deadlock and rolls back one transaction; applications typically receive MySQL error 1213 and should safely retry the transaction. To diagnose a deadlock, start with SHOW ENGINE INNODB STATUS; for recurring incidents, use innodb_print_all_deadlocks and Performance Schema data_locks and data_lock_waits to investigate lock relationships. Common causes include inconsistent transaction ordering, long-running transactions, and inefficient indexing or locking patterns. The most effective fixes are to keep transactions short, access shared resources in a consistent order, optimize the indexes used by locking statements, and implement safe retry handling.

  396 views
MySQL Consulting vs In-House DBA: Which Is Right for Your Team?

Choose an in-house DBA when you need continuous database ownership, deep knowledge of internal systems, and day-to-day operational control. Choose MySQL consulting when you need specialized expertise, performance tuning, migrations, complex troubleshooting, or additional database capacity without hiring a full-time specialist. A hybrid model can be the best fit when your team handles routine database operations internally but needs external expertise for complex projects, peak workloads, or specialized MySQL problems. The right choice depends on workload consistency, technical complexity, required coverage, internal expertise, scalability, and total cost—not simply the hourly or salary cost. Mafiree's managed database services provide ongoing MySQL support alongside specialized database expertise for organizations that need more flexibility than a purely in-house model.

  274 views
MySQL Consultant: When to Call in a Performance Expert

Most MySQL slowdowns are fixable in-house. A smaller set of problems keep coming back, keep growing, or sit outside what routine tuning can solve — and that's the line worth knowing before an incident forces the decision for you.

  352 views
MySQL Performance Issues: 7 Signs You Need Professional Tuning

MySQL performance issues are rarely sudden — they build over time through slow queries, InnoDB buffer pool misses, replication lag, lock contention, thread pile-ups, tablespace bloat, and unstable query plans. This post identifies the seven most reliable signs that your MySQL environment needs professional DBA attention, with diagnostic queries and remediation guidance for each.

  13225 views
MySQL Schema Migration Without Downtime: A Real Fintech Case Study

Schema changes on large MySQL tables can bring production systems to a halt if not handled correctly. This case study walks through how Mafiree helped a fintech client execute a zero-downtime MySQL schema migration on a 500M+ row production database — covering the real challenges faced, the three-phase tool strategy using gh-ost, pt-online-schema-change, and MySQL 8.0 INSTANT DDL, production configuration settings with performance benchmarks, and best practices for safely evolving your MySQL schema without impacting users

  4346 views
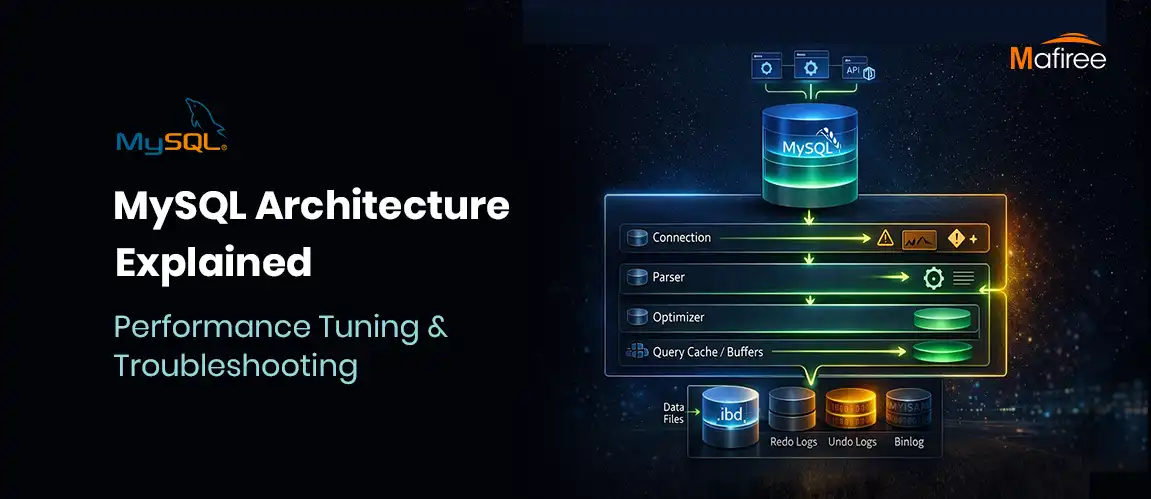
MySQL Architecture Explained: Performance Tuning & Troubleshooting Guide

MySQL features a unique tiered architecture that separates query processing from data storage through its pluggable storage engine model. This guide explores the core components—from connection handling and the SQL optimizer to the physical storage of data on disk. By understanding how engines like InnoDB provide ACID compliance and row-level locking, you can significantly improve your database's scalability. We also break down the query execution workflow and provide actionable tips for performance tuning, such as optimizing the buffer pool. Whether you're managing a replica set or a standalone instance, mastering MySQL’s internal structure is essential for building high-performance applications.

  2302 views
MariaDB vs MySQL: What's Different in 2026 and Which One Should You Use

Discover how MariaDB 11.x is redefining open-source databases with cutting-edge features like system-versioned tables, native AI-ready vector support, UUIDv7 for scalable inserts, and enterprise-grade security; all in the Community Edition, without the paywall.

  1739 views
MySQL’s Connection Control Plugin for Brute-Force Protection: A DBA Security Guide

“Fortify Your MySQL Security: Slow Down Attackers with Connection Control Plugin” Learn how the MySQL Connection Control Plugin helps defend against brute-force login attempts by introducing intelligent, progressive delays—without locking out legitimate users.

  13203 views
MySQL 8.4 Migration: Key Changes for IT Leaders

Explore the 8 critical changes in MySQL 8.4 you need to know before migrating your production environment. From authentication updates to InnoDB defaults, this release brings significant operational implications for developers and DBAs.

  295 views
Load Balancing in MySQL: Read and Write Traffic Optimization Using MySQL Router

Optimize MySQL traffic with MySQL Router — smart load balancing made easyRouter Architecture image widget

  1976 views
Check Constraints in MySQL

Master Database Integrity with Check Constraints: Improve Data Quality and System Performance

  13201 views
Guarding Your Account: 5 Essential Tips to Evade Common Password Mistakes.

How to Secure your mysql database with the mysql validate password component

  3568 views
Access Control & Account Management In MySQL 8

Discover how MySQL 8 enhances security through features like password expiry, password validation, account lock/unlock, privilege management, and dual passwords. Safeguard your valuable data and streamline access control in your MySQL environment.

  3891 views
Significance of using Invisible Primary key (GIPK) with MySQL 8.0

How Generated Invisible Primary Keys (GIPK) Can Boost Your Database Efficiency

  3732 views
Optimize Your Database: Exploring MySQL 8.0 JSON Functions

This blog highlights the some of the important JSON function in MySQL 8.0 with examples. Level up your SQL skills with MySQL 8.0's JSON functions.

  5168 views
Best practices on enabling Audit log on MySQL, MariaDB and ProxySQL

Importance of audit log in MySQL, MariaDB and ProxySQL. Best practices to enable audit log

  5201 views
High Availability for MySQL using Orchestrator and ProxySQL

Auto slave promotion without any DBAs intervention using Orchestrator and ProxySQL. If you are looking for a HA solution without going for synchronous replication or Aws RDS then Orchestrator with ProxySQL is a great choice.

  3494 views
Understanding the Spider Storage Engine

MariaDB Spider is a storage engine that supports federation and sharding across multiple MySQL or MariaDB servers. It helps distribute data and workloads, making it useful for scaling large datasets, balancing traffic, and improving data retrieval through parallel processing.

  1763 views
Avoid deadlocks, certification failures on Galera Cluster using ProxySQL

Dealing with deadlocks, certification failures on Galera cluster by running single node writer using ProxySQL

  7097 views
MySQL Character Set: UTF8MB4 vs UTF8 and How to Choose the Right Encoding

Choosing the right MySQL character set is critical for ensuring accurate data storage, multilingual support, and proper text comparison. While the legacy utf8 (utf8mb3) character set supports only up to 3-byte characters, it fails to handle modern Unicode requirements such as emojis and certain international symbols. In contrast, utf8mb4 provides full 4-byte Unicode support, making it the recommended standard for modern applications. This guide explains the differences between UTF8MB4 and UTF8, their impact on storage and performance, and provides step-by-step instructions to configure and migrate your MySQL databases safely.

  5861 views
Real time data streaming from MariaDB to Columnstore

How real time data from transactional database(mariadb) to analytic database(columnstore) is achieved using MariaDB's maxscale binlog streaming

  1497 views
Fixing the MariaDB Galera Bug: WSREP Lock Waits

A MariaDB Galera cluster can experience severe stalls when concurrent updates to the same primary key trigger an unexpected deadlock issue. This blog explains how we reproduced the issue in MariaDB 10.2, why the affected node became unresponsive, and the recovery and upgrade options used to resolve it.

  4585 views

Subscribe for email updates

Get in touch with us

Highlights

More than 6000 Servers Monitored

Happy Clients

Certified DBAs

24 x 7 x 365 Support

PCI

Database Services

MySQL MongoDB PostgreSQL SQL Server Aerospike Clickhouse TiDB ScyllaDB

Quick Links

Careers Blog Contact Privacy Policy Disclaimer Policy

Contacts

Linkedin Mafiree Facebook Mafiree Twitter Mafiree

Nagercoil Office

Miru IT Park, Vallankumaranvillai,

Nagercoil, Tamilnadu - 629 002.

Bangalore Office

Unit 303, Vanguard Rise,

5th Main, Konena Agrahara,

Old Airport Road, Bangalore - 560 017.

Call: +91 6383016411

Email: sales@mafiree.com


Copyright © - All Rights Reserved - Mafiree